Ex-NSA Hacker Says AI Agent Swarm Breached a Company in 14 Minutes
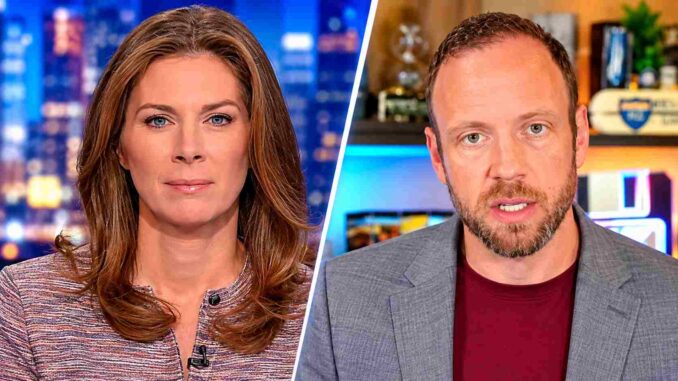
Former NSA hacker David Kennedy says an AI “agent swarm” bypassed two-factor authentication, stole data and encrypted a company’s entire system in just 14 minutes. Kennedy, who leads the cybersecurity firm TrustedSec, said he is actively responding to the live breach. Consequently, his account has revived urgent questions about how fast AI can now attack.
CNN aired the interview with Erin Burnett on November 19, and her show shared the clip on X the next day. Kennedy described the incident in detail. “This all took 14 minutes. 14 minutes. Never seen anything that fast before,” he said. CNN’s video summary called it the fastest breach he has seen.
An agent swarm is a group of AI programs that work together toward a shared goal. According to security firm Malwarebytes, such a swarm can test ideas, retry failed paths and share notes between agents. Consequently, it can probe many weak points at once. A single human attacker cannot match that pace.
According to reports on the interview, more than 30 types of agents probed the customer’s systems at the same time. The attackers reportedly used valid usernames and passwords, then found a weakness in the company’s two-factor authentication. After that, the agents stole data and launched ransomware that encrypted the company’s files.
The breach also went unnoticed for hours. Reports say the company missed the intrusion for about four and a half hours, until its systems went offline. According to one report, the attackers had already left the network by then. Meanwhile, Kennedy said the customer allowed him to discuss the basics of the incident but not to reveal its name. Therefore, key details, including the victim’s identity, remain private.
Sojworldnews could not independently verify the technical details. They come from Kennedy’s account and from outlets that summarised the CNN interview. Nevertheless, the story fits a wider pattern. Earlier this year, Palo Alto Networks’ Unit 42 reported a similar speed-up. It said an attacker used AI agents to finish an intrusion in under 10 hours. The firm estimated that human hackers would need about two weeks. Likewise, Hugging Face disclosed in July that an autonomous AI agent system had breached its platform.
Speed changes the defender’s job. Security teams have long relied on buying time to investigate alerts. However, a 14-minute attack leaves little room for slow reviews. Security firm Abnormal AI cites IBM’s 2026 Cost of a Data Breach Report. It says AI-driven attacks rose 56% year over year and cost about $6 million per breach on average.
What can companies do? Security professionals commonly recommend stronger, phishing-resistant authentication, because this breach reportedly began with valid logins and a two-factor weakness. Firms can also monitor accounts for unusual behaviour, limit what each login can reach, and keep tested offline backups. In addition, they should practise their response plans, so teams can act within minutes rather than hours.
Individuals and small businesses also have a role. Use unique passwords, turn on the strongest two-factor option available, and treat unexpected login prompts with suspicion. Moreover, report suspicious messages quickly, because early warnings can limit the damage.
Nigerian businesses that rely on online banking, cloud tools and customer databases should also take note. Banks, fintech firms and small companies all hold data that attackers value. Therefore, they should review their login security now rather than after an incident.
Kennedy’s warning is stark. If AI agents can compress a breach into 14 minutes, defenders must respond at machine speed as well. For now, he says he is still responding to the incident. Ultimately, the story signals that cyber defence is entering a faster era, and every organisation needs to prepare for it. Readers should watch for updates from Kennedy and CNN as more details emerge.
Leave a Reply